Start by listing what your business cannot run without, then work out how long you could survive losing each item and how much recent work you could afford to lose.
For most small businesses, a restore test once a quarter is the minimum, and monthly testing makes sense when your data changes every day or the files are hard to replace.
The mistake that costs businesses the most is assuming a backup works because the software says it ran, when they have never tried restoring from it.
Most small businesses need both a local backup for fast restores and a cloud backup for the disasters that can destroy everything in one building, but if you can only pick one,…
With backups you have actually tested, most of the recovery time goes to cleaning up infected machines and checking your data, and the restore itself is often the shortest part.
A cloud backup is only worth something if you can actually get your files or systems back out of it, and the only way to know that is to restore from it on purpose.
Recovery time objective (RTO) is the longest your business can run without a system, and recovery point objective (RPO) is the most recent data you can afford to lose, and both…
A backup that's never been restored is just hope, not insurance.
Email filters are effective against bulk threats but leave your team vulnerable to targeted attacks that look legitimate.
Password managers cut your breach risk dramatically by making the single attack that compromises most accounts nearly impossible to pull off.
Small dental and medical offices are covered by HIPAA, but the rules aren't as complicated as they seem if you focus on what actually matters.
Employee mistakes cause most breaches, but you can train people to spot and stop them.
Paying a ransomware demand often seems like the fastest solution, but it usually makes the problem worse.
Multi-factor authentication stops most account takeovers, but rolling it out takes planning to avoid frustrating your team.
Before a cyber insurer writes your policy, they want proof of a handful of specific security controls. Here is what they ask about, why each one matters, and how to get ready…
Fake emails impersonating Microsoft and Amazon are among the most effective phishing attacks, but a few specific checks catch most of them before they do damage.
Most companies discover their security has real gaps only after something goes wrong.
The companies that survive ransomware attacks almost always had three specific things in place beforehand.

Your first month with a managed IT partner typically spans discovery of your systems, deployment of monitoring and security tooling, backup verification, and fixes for urgent…
A slow helpdesk isn't a minor inconvenience—it's a drain on your whole business that compounds every single day.
The right choice depends on your company size, growth stage, and how much IT complexity you actually have.
24/7 monitoring catches problems before they interrupt your day by watching your systems around the clock and responding to threats in minutes, not business hours.
The right IT support model depends on your business size, growth rate, and how much downtime costs you.
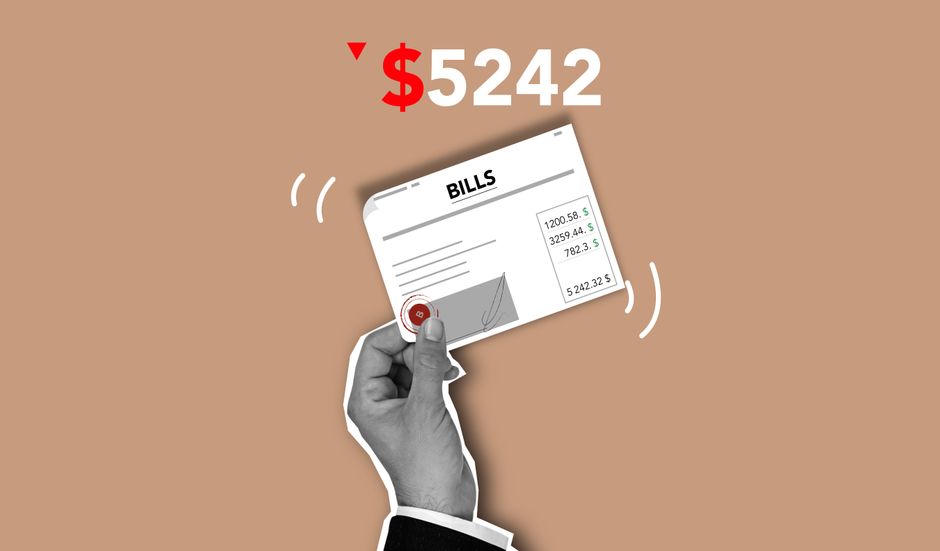
Five minutes of downtime isn't a minor glitch. It's a measurable hit to your revenue, reputation, and team productivity.
Your business won't collapse if your IT person leaves, and you can prepare so it never becomes a crisis.
A restore from backup is straightforward if you've tested it beforehand, and chaotic if you haven't.
Ninety percent of breaches start with a click. Teach your team these five tells and stop most attacks at the front door.
Most businesses think they're protected until they need to restore. Here's the simple rule that separates hope from a real recovery plan.